What Is Sovereign AI?
The models are working, but the answer to "where does this data actually live, and who can touch it?" is no longer comfortable. Every prompt that leaves the boundary, every weight held by a third party, and every model update applied by someone else is a dependency the business now has to defend. For a team that handles regulated data or treats its models as IP, the dependency stops being an abstraction and starts being a liability.
Sovereign AI is the ability of an organization to control where its AI data resides, where and how its models compute, and who can access, change, or audit the system. In practice, it means running AI inside an infrastructure boundary the organization controls, rather than inside a third party's cloud.
The term also covers nations and regions. The European Commission's Cloud and AI Development Act is intended to strengthen Europe's sovereignty and competitiveness in the cloud and AI ecosystem. For an executive team, the practical question is narrower: can the business run valuable AI inside a boundary it controls, while keeping the flexibility to choose models and tools?
| Deployment mode | Control and boundary | Where it runs | Typical buyer |
|---|---|---|---|
| Public cloud | Provider controls infrastructure and terms | Provider's data centers, optionally in a chosen region | Product teams, low-sensitivity workloads |
| Private cloud | Dedicated to one organization, often provider-operated | Dedicated resources, internally or by a provider | Compliance-driven workloads |
| On-premises | Organization controls racks, power, and network | Organization's own data center | Data centers, edge sites, restricted facilities |
| Air-gapped | Maximum: no outside network paths | Network physically isolated from unsecured networks | Defense, classified, critical infrastructure |
The step a team takes depends on the workload, not on ideology: the stronger the control a data class needs, the further up this table the workload belongs.
Three things that must be under control
Sovereign AI is not one feature. It is a bundle of three control questions, and a system is only as sovereign as the weakest answer.
- Data residency. Data residency is the geographic or physical location of data, identified by the country or region that houses the data centers, servers, or other infrastructure that processes and stores it. For AI, the question extends to prompts, retrieved documents, training data, and model outputs: where do they live during inference, and where are backups and logs written?
- Compute and model residency. Where does inference actually run, and who holds the model weights? A model called through a third-party API is sent to the provider’s endpoint and runs on the provider’s hardware, with prompts and outputs passing through the provider’s infrastructure.
- Governance. Who can access the system, who approves model changes, and what evidence exists of what the system did? Governance is what lets an audit trail answer a regulator’s question, not just a sales call.
A useful litmus test: geography is not sovereignty. A model hosted in-country but reached through a vendor’s API is still under the vendor’s control over updates, terms, and access. Data sovereignty is the data side of this idea; sovereignty adds control over the models, infrastructure, and people involved. The sovereign AI reference architecture lays out how that control is structured in practice.
Why executives care
Four forces push AI decisions up to the executive layer.
Compliance is becoming binary. The EU AI Act entered into force on 1 August 2024 and phases in over time; the remainder of the Act starts to apply on 2 August 2026. Under the GDPR, transfers of personal data to a third country may take place only where the safeguards in Chapter V are complied with, which shapes where EU personal data can be processed. In healthcare, HIPAA covered entities are healthcare providers, health care clearinghouses, or health plans that conduct electronic transactions, and business associates that create, receive, maintain, or transmit protected health information must operate under a business associate agreement. In the power sector, NERC CIP compliance means meeting the Critical Infrastructure Protection (CIP) standards issued by the North American Electric Reliability Corporation (NERC), which establish mandatory cybersecurity and physical security requirements for systems that support the Bulk Electric System (BES). For federal workloads, the Federal Risk and Authorization Management Program (FedRAMP) is a United States federal government-wide compliance program that provides a standardized approach to security assessment, authorization, and continuous monitoring for cloud products and services.
Supply-chain risk. The European Commission has stated that over-reliance on non-EU cloud service providers poses a significant risk to digital autonomy and resilience. The same dynamic applies inside the enterprise: a model whose updates, pricing, or availability sit outside the organization is a dependency, not an asset. The set of rules that is hardening into the default for sovereign deployments is summarized in the rules for sovereign AI in 2026.
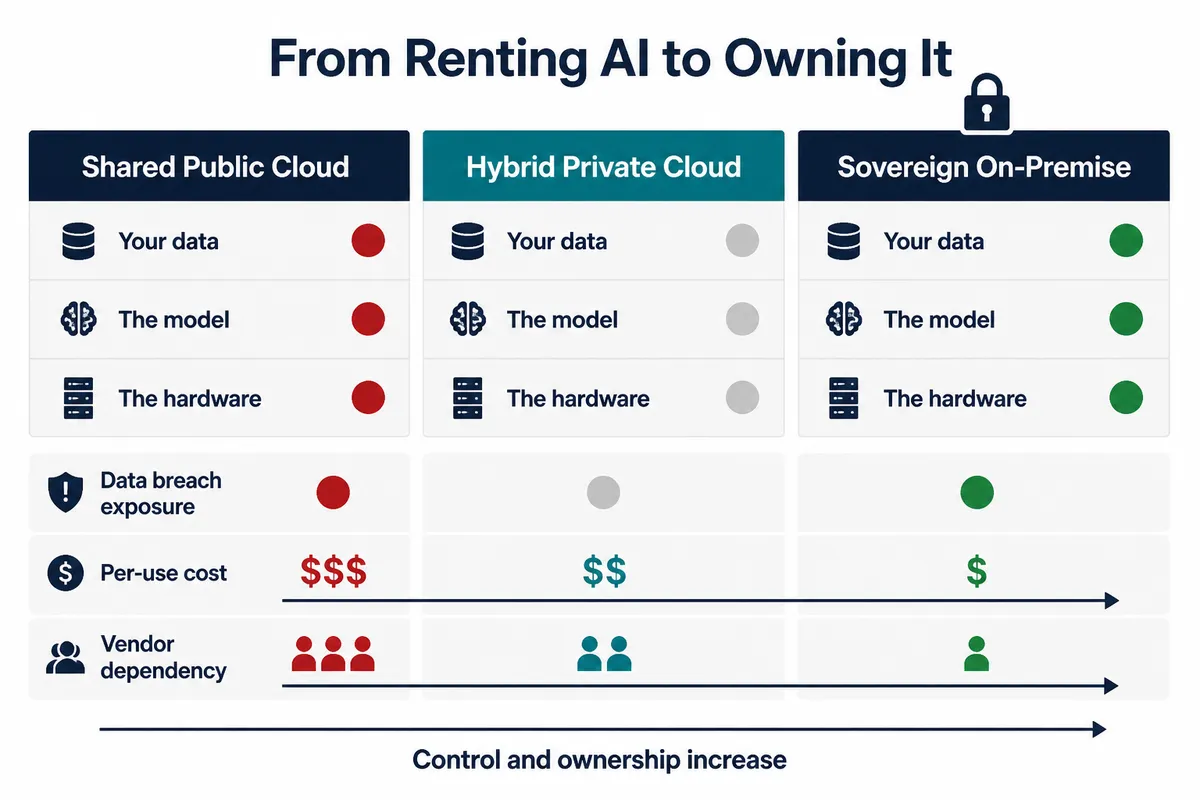
Predictable cost. Sovereign deployments convert variable per-token spend into owned capacity with a steadier cost profile. The accounting trades a usage-based operating expense for a capital-heavy, more predictable one; whether that suits the business depends on how steady the workload is.
Intellectual property. In manufacturing, defense, and research, the models and data are the IP. Processing them through external services hands a copy to the vendor, whether intended or not.
The sovereignty spectrum
Sovereignty is a spectrum, not a switch. Four deployment models cover most of the range, in ascending order of control.
- Public cloud. Shared multi-tenant infrastructure operated by a provider, with the cheapest cost per unit and the fastest deployment. Residency commitments exist, but physical control belongs to the provider.
- Private cloud. A cloud computing environment in which all hardware and software resources are dedicated exclusively to, and accessible only by, a single organization. Many organizations choose it as the simplest, or the only, way to meet regulatory compliance requirements.
- On-premises. The same workloads, but inside the organization’s own data center, with physical control of racks, power, and network.
- Air-gapped. A network security measure that ensures a secure network is physically isolated from unsecured networks, with no network interfaces connected to outside networks.
On-premise AI and air-gapped operation sit at the high-control end of this spectrum; AI factories are the industrial pattern that standardizes how such capacity is built and operated.
Each step to the right buys control and gives up something: cost per unit, deployment speed, and ease of updates.
Named deployment topologies
In vendor and procurement language, the spectrum shows up as named topologies:
| Topology | What it is | Typical buyer |
|---|---|---|
| Public cloud AI | Models and data on shared provider infrastructure, possibly in a chosen region | Product teams, low-sensitivity workloads |
| Sovereign / dedicated cloud | Provider-operated, region-restricted or single-tenant cloud | Regulated data that must stay in-country |
| Private cloud | Dedicated infrastructure serving a single organization, hosted internally or by a provider | Compliance-driven workloads |
| On-premises AI | AI on hardware the organization operates in its own data center | Data centers, edge sites, restricted facilities |
| Air-gapped AI | AI on networks physically isolated from unsecured networks | Defense, classified, critical infrastructure |
The cost, control, and compliance tradeoff table
| Model | Cost profile | Control | Compliance posture | What it gives up |
|---|---|---|---|---|
| Public cloud | Lowest per unit; pay-as-you-go | Infrastructure controlled by the provider | Requires cross-border transfer safeguards for regulated data | Physical control, audit independence |
| Private cloud | Moderate; dedicated resources, cloud-style operations | Dedicated to one organization | Strong for many regulatory requirements | Still provider-operated in many offerings |
| On-premises | High capital cost, predictable operating cost | Full physical control | Eases in-country residency requirements | Slower deployment; operations burden on the organization |
| Air-gapped | Highest; isolation plus manual change paths | Maximum; no outside network paths | Meets the strictest isolation requirements | No live updates; changes move across the gap physically |
The air-gapped row deserves a sentence on its own: because an air-gapped network has no network interfaces connected to outside networks, software cannot automatically self-update, and updates must be installed manually, with data and new versions carried across the gap on removable media. That is the real price of the strongest isolation, and it is why the update path is a legitimate evaluation question.
How sovereign AI differs from generic enterprise AI
Generic enterprise AI is about adopting AI across functions to support organizational goals, combining technology, processes, and people. Sovereign AI is a subset with an additional constraint set: the workload must run inside a defined infrastructure and governance boundary.
The two lenses select for different things. A generic enterprise AI evaluation weighs accuracy, per-token cost, and developer experience, and calling an external model API is a perfectly rational choice. A sovereign AI evaluation weighs where inference executes, who can access prompts, weights, and outputs, and how the organization proves what happened. An enterprise can be running both: high-volume, low-sensitivity workloads on public models, and regulated or sensitive workloads on sovereign infrastructure. The distinction is about workload classification, not ideology.
The practical consequence: procurement questions change. Instead of only “what does it cost per token?”, the evaluation asks “who holds the weights, where do the prompts live, and what evidence does an auditor see?” That is why sovereign AI belongs in the same conversation as regulated AI: regulation is usually what defines the boundary, and the deployment model is how the organization meets it.
Who needs it most
- Defense and aerospace. Classified and controlled workloads, export controls, and partner-agreement restrictions that limit what may touch foreign networks or vendors.
- Healthcare. Protected health information under HIPAA, payer and research agreements, and patient-trust expectations that push processing inward.
- Nuclear, energy, and utilities. Grid-critical systems under NERC CIP, plus physical security and audit evidence requirements that extend to the systems that support operations.
- Manufacturing and factories. Process knowledge, yield data, and quality models as trade secrets; production networks that are often already segmented from the internet.
- Government and public sector. FedRAMP authorization for cloud services holding federal data, and a general expectation that sensitive processing stays inside the national boundary.
- Finance and insurance. Cross-border transfer rules, model risk management, and audit demands on anything that influences a decision.
The common thread is not industry but consequence: when the data is regulated, the model is IP, or an outage is a safety event, the boundary is the business case.
How to evaluate a sovereign AI platform
A short checklist that turns “sovereign” from a marketing adjective into a procurement test, and a fuller walkthrough of what to probe is in how to evaluate sovereign AI platforms:
- Data residency, end to end. Ask where sensitive data is during training, inference, backup, and logging, and who can access each copy. Accept named locations and named roles, not adjectives.
- Model control. Confirm that model weights stay inside the boundary, that models can be replaced or rolled back without rebuilding the application, and that the organization can audit which model produced which output.
- Air-gap proof, if claimed. Request the network architecture and evidence that no network interfaces connect to outside networks. Ask how updates are staged and moved across the gap.
- Compliance attestations. Collect named certifications and sample audit exports; a platform that cannot produce the evidence it claims to keep is telling you something.
- Exit path. What happens to data, models, and integrations if the relationship ends? Lock-in is a sovereignty issue, not just a pricing issue.
- Total cost over three years. Compare owned capacity against usage-based spend, including engineering time and compliance effort. Predictability is the benefit; make sure it is real for the workload shape.
The goal is not to reach the most extreme point on the spectrum. It is to place each workload where its risks, regulations, and economics point, and to be able to explain that placement to a board, an auditor, or a regulator.
A working demonstration of a sovereign AI platform shows what the boundary looks like in operation: data, models, and workflows running inside the organization’s infrastructure, with the audit trail to prove it. Request a demo of Shakudo.
Last verified: 2026-09-05
Why CTOs and CISOs in Regulated Industries Choose Shakudo to power their sovereign AI strategy
-
Data sovereignty by architecture
Prompts, outputs, weights, and compute run inside the infrastructure boundary the organization controls, so residency and access follow the data class rather than a provider's region choice.
-
Vendor-agnostic orchestration
The orchestration layer routes across models and serving backends without tying the deployment to one provider, so models can be replaced or rolled back without rebuilding the application.
-
Audit-ready operations
Access, model changes, and generation history are recorded so the system can answer a regulator's question about what it did, not just a sales call.
-
A path from on-prem to air-gapped
The same platform supports on-premises and air-gapped postures, so a team can start where the economics justify and tighten isolation as the requirement demands.

Frequently asked questions
How does sovereign AI differ from on-premises and air-gapped deployment?
Sovereignty is a spectrum of control over where data and compute live and who can audit them, not a single deployment. On-premises and air-gapped are points on that spectrum, with air-gapped at the high-control end. Sovereign AI is the requirement to control all three, data residency, compute and model residency, and governance.
Does sovereign AI mean the hardware has to be domestic?
Not by itself. Geography is not sovereignty. A model hosted in-country but reached through a vendor's API is still under the vendor's control over updates, terms, and access. Sovereignty adds control over the models, infrastructure, and people involved, not just where the servers sit.
What are the cost implications of a sovereign deployment?
Sovereign deployments convert variable per-token spend into owned capacity with a steadier, more capital-heavy profile. Whether that suits the business depends on how steady the workload is, because the accounting trades a usage-based operating expense for a capital one.
When is sovereign AI overkill?
For high-volume, low-sensitivity workloads, calling an external model API is a perfectly rational choice and full sovereignty is not justified. The question is workload classification: regulated, sensitive, or IP-bearing workloads point to a sovereign boundary, while general workloads can run on public models.